 LIVESave the World, live from Salt Lake City during KubeCon · Wed Nov 11, 11:00 MT →

The agent your security team will approve.
Your developers want agents. Your security team wants to know exactly what they do, where they run and who signed for it. Infrared answers both.
Agents run in your account, on your model key, inside a network fence. Your platform team writes the opinions every agent follows. A person approves every merge and every promotion, and every step leaves a record.
What it's like.
- week one
You write the rules once.
Each AgentRole's guidance is written as your org's opinions: how to test, what's off limits, what a security review must check. Your platform team edits them in the app, and every agent follows them.
- week one
Access follows your directory.
Access groups map Google Workspace groups and GitHub logins to roles. Roles follow your groups within minutes, and Infrared fails closed if it can't read them.
- every change
Nothing ships unreviewed.
Every Change runs the required steps: build, security review, end-to-end verification, a person's approval and merge. A blocking verdict stops it, whoever wrote it.
- every day
The watchers watch.
Daily security, performance and SRE audits open issues for what they find, de-duplicated so the backlog stays readable.
- audit day
You show the record.
Every run, merge, approval, deployment and rollback is in one log, with who did it, what the agent saw, what it cost and the evidence it captured.
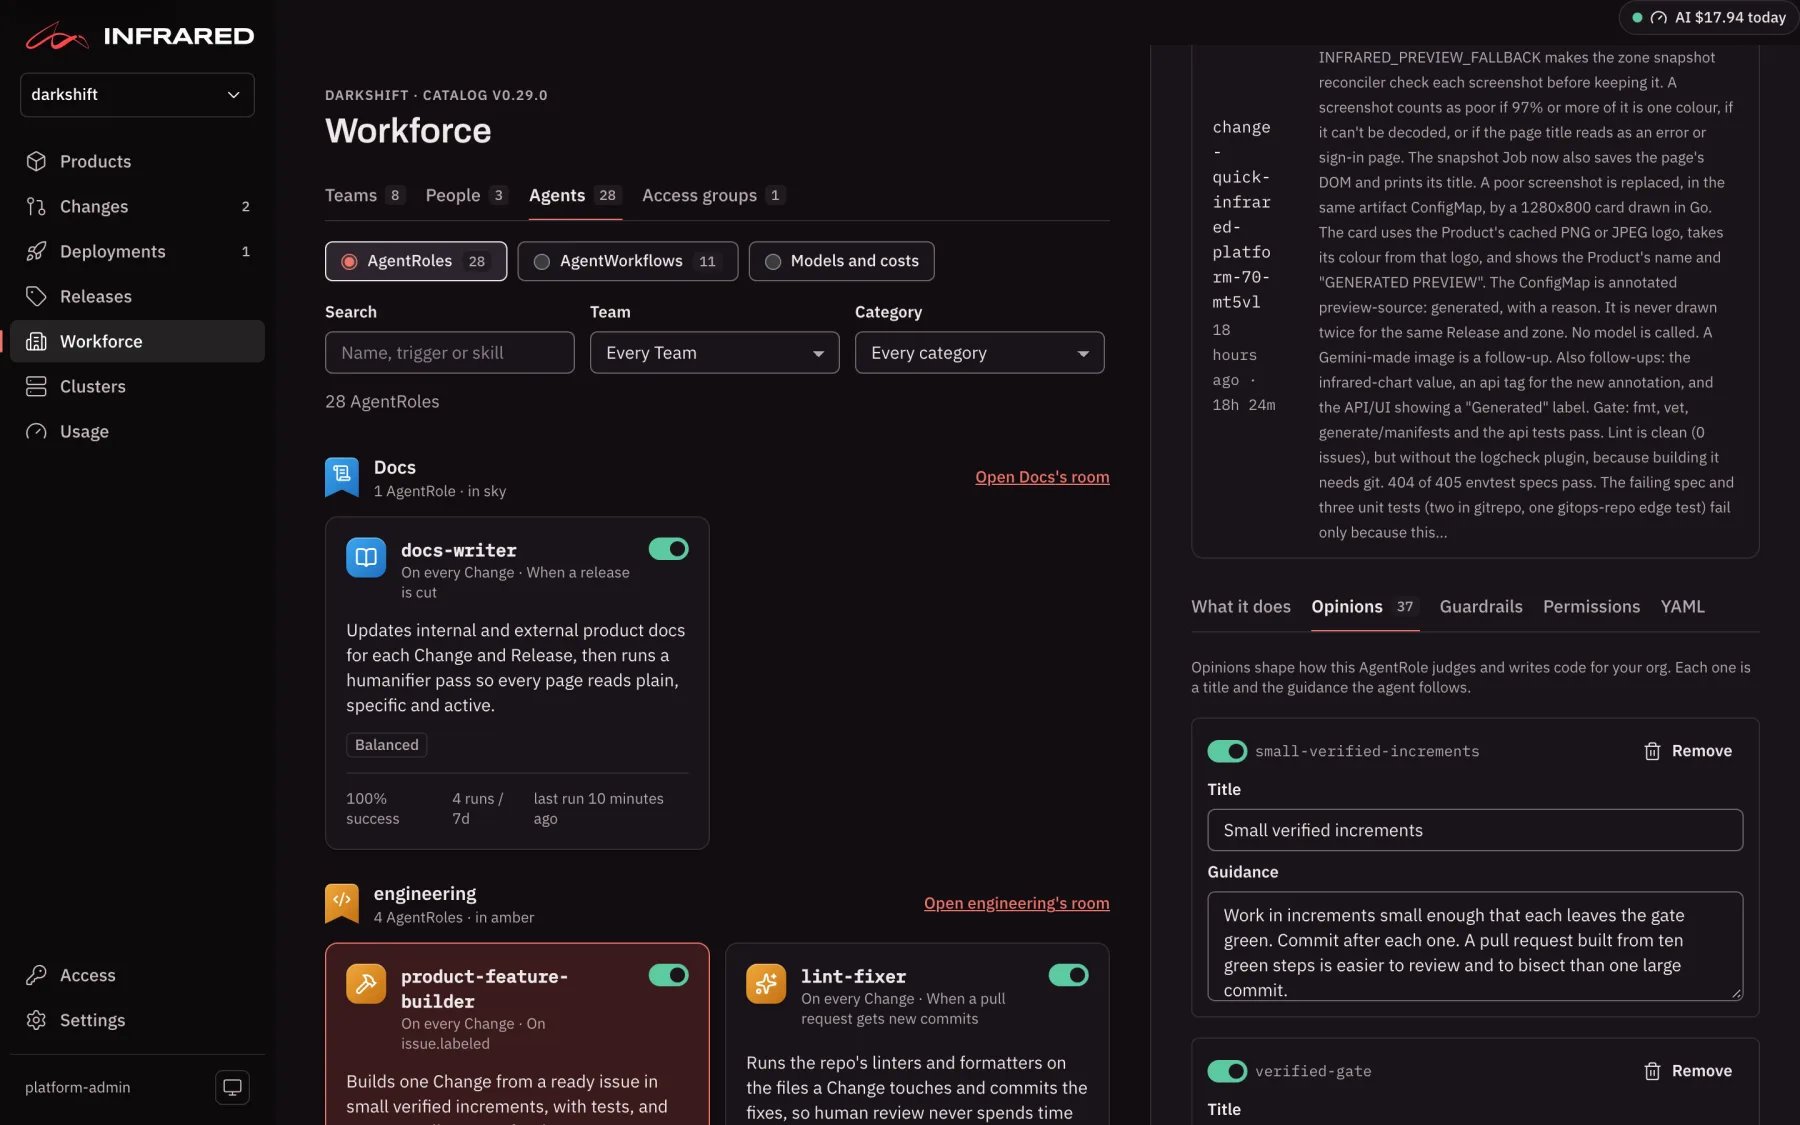
What Infrared does for you.
Your control plane, your rules.
Run Infrared on your own GKE or EKS cluster, wired to your Google Workspace groups, your GitHub organization and your clouds.
Not quite you?
Infrared serves every one of these teams with the same factory. Read the story closest to yours.
Bring agents in, the right way.
Become a design partner: we'll stand Infrared up in your account with your platform team, and take a real Change through your controls.